Raven - Audit Your Email Encryption Without Sending a Single Packet
Most of the world's email still travels like an open letter. Raven passively observes your mail traffic, verifies whether every hop was cryptographically sealed, and produces a confidence-bounded posture score with court-grade forensic receipts.
⚠ 1 hop chain unobservable (TLS 1.3)
STARTTLS stripped by peer relay
Claimed: enforce · Observed: plaintext
4 MTAs support Hybrid Kyber-768
TRANSIT HOP TOPOLOGY & WEAKEST LINK PINPOINT
OBSERVED ENCRYPTION RATIO
FORENSIC EVIDENCE & FINDINGS CHAIN
Audit-ready drilldown with exact packet offsets| SEVERITY | RULE ID | AFFECTED HOST | EVIDENCE OFFSET | VERDICT | HASH SIGN |
|---|---|---|---|---|---|
| CRITICAL | SMS-STRIP-001 | mail.legacy-corp.org:25 | Pkt #1,429 [0x04f2] | STARTTLS announcement suppressed | sha256:4a8b1... |
| HIGH | SMS-X509-004 | relay-hub.net:587 | Pkt #842 [0x01a8] | Cert CN mismatch (claims old.internal) | sha256:7c91e... |
| MEDIUM | SMS-ENF-002 | mx-backup.gov.in:25 | Pkt #1,104 [0x08b4] | MTA-STS policy enforce violated | sha256:3d28f... |
Passively verifies cryptographic posture across enterprise MTAs and mail relays
Why Email Transit Security is Broken in the Wild
The Internet was built ~50 years ago where email was designed as an open postcard. Sealing the envelope via STARTTLS is purely voluntary — and in the wild, active attackers silently strip the seal without your knowledge.
of global mail servers present invalid or expired X.509 identity certificates
Active Port Scanners
Intrusive & blocked by firewalls
Passive Observation
100% Non-intrusive & silent
Without passive cryptographic observation, your organization remains blind to
STARTTLS Stripping Attacks
Handshake Command Injection
Silent Plaintext Downgrades
Weak Ciphers & Nonce Reuse
MTA-STS & DANE Drift
SPF, DKIM, and DMARC verify sender identity — they do not guarantee encryption in transit.
Everything You Need to Audit Mail Cryptographic Posture
0–100 Confidence-Bounded Posture Score
Deterministic mathematical scoring engine based on NIST SP 800-52r2 and RFC standards. Raven produces an honest score with statistical confidence bands and explicitly declared blind spots — never a black-box guess.
Cross-Hop Delivery Graph
Trace the complete journey of your email across every MX hop and relay. Raven calculates traffic-weighted exposure and instantly highlights the single weakest link.
Downgrade Radar
State-machine analysis of SMTP handshakes to detect active STARTTLS stripping, command injection, and cipher downgrade anomalies before they cause a breach.
Court-Grade Forensic Evidence Chains
Every finding links directly to the exact flow timestamp, packet number, byte offset, and TLS record index. Backed by SHA-256 signed evidence chains that stand up in legal, regulatory, and forensic security audits.
Claim vs. Reality Audit
Compares published DNS policies (MTA-STS, DANE TLSA, TLS-RPT) against real wire traffic. Raven alerts you when an advertised security policy fails in actual transit.
Interactive Incident Replay
Step-by-step forensic animation replaying flagged sessions. Visually inspect when and where negotiation downgraded with exportable WebM evidence recordings.
Air-Gapped & Sovereign Ready
Zero external cloud dependencies. Unplug the network cable, upload a PCAP, and run complete forensic evaluations on isolated defense and enterprise workstations.
Why Security Teams Trust Raven
Designed from first principles to fulfill rigorous defense requirements: non-intrusive observation, transparent math, and courtroom-admissible evidence.
What Makes Raven Different
Zero Active Probing
We never knock on servers or send packets. Raven operates as a pure passive observer, safe for covert military and enterprise SOC environments.
Honest Uncertainty
When encryption hides details (like encrypted certificates under TLS 1.3), we declare blind spots rather than pretending everything is fine.
Court-Grade Receipts
Every score, flag, and finding comes with the exact packet offset, byte range, and hash-signed span. No hunches, no opaque numbers — only audit-admissible proof.
Posture Decay Timeline
Monitors cryptographic degradation across time windows. Alerts when a relay drifts from Grade A to Grade D before it is compromised.
100% Offline & Deterministic
Run on air-gapped laptops without internet. The exact same PCAP with the same package version produces bit-for-bit identical report checksums.
Self-Hosted Air-Gapped Deployment
Raven is self-hosted software that runs entirely within your perimeter. No cloud dependencies, no credential handovers, and 100% passive.
Analyst Workstation
Single-analyst laptop or incident-response rig. Drag-and-drop PCAP ingest and offline evidence generation.
100% self-hosted on your hardware. Zero data ever leaves your perimeter.
Validated by Security Teams
& Forensics Leads
Abhishek Kulkarni
Lead SOC Analyst, Sovereign Cyber Defense
“Raven gave our SOC team immediate passive visibility into stealth STARTTLS stripping attacks that our boundary firewalls completely missed. Zero packets sent to external targets.”
Vikram Malhotra
Digital Forensics & Incident Response (DFIR)
“The court-grade evidence chain linking each security finding to the exact packet offset, byte range, and hash signature makes compliance auditing completely unassailable.”
Sneha Nair
Enterprise Infrastructure & Mail Architect
“The Cross-Hop Delivery Graph immediately highlighted that our secondary fallback MX had quietly disabled TLS 1.3. We fixed it with the copy-paste Postfix playbook in 5 minutes.”
Rohan Deshmukh
Security Compliance Auditor
“The deterministic RFC and NIST scoring rubric with honest confidence intervals is refreshing. It tells us exactly what was unobservable instead of handing out false all-clears.”
Rohan Deshmukh
Security Compliance Auditor
“The deterministic RFC and NIST scoring rubric with honest confidence intervals is refreshing. It tells us exactly what was unobservable instead of handing out false all-clears.”
Sneha Nair
Enterprise Infrastructure & Mail Architect
“The Cross-Hop Delivery Graph immediately highlighted that our secondary fallback MX had quietly disabled TLS 1.3. We fixed it with the copy-paste Postfix playbook in 5 minutes.”
Vikram Malhotra
Digital Forensics & Incident Response (DFIR)
“The court-grade evidence chain linking each security finding to the exact packet offset, byte range, and hash signature makes compliance auditing completely unassailable.”
Abhishek Kulkarni
Lead SOC Analyst, Sovereign Cyber Defense
“Raven gave our SOC team immediate passive visibility into stealth STARTTLS stripping attacks that our boundary firewalls completely missed. Zero packets sent to external targets.”
Frequently Asked
Questions
Everything you need to know about Raven's passive observation principles, cryptographic methodology, and air-gapped deployment.
What is Raven and how does it work?
Does Raven connect to our mail servers or read email contents?
Why is passive observation better than active scanning?
Can Raven operate in air-gapped or classified environments?
What makes Raven's posture score trustworthy?
How does Raven detect STARTTLS stripping and downgrade attacks?
Stay Ahead with Cryptographic
Email Insights
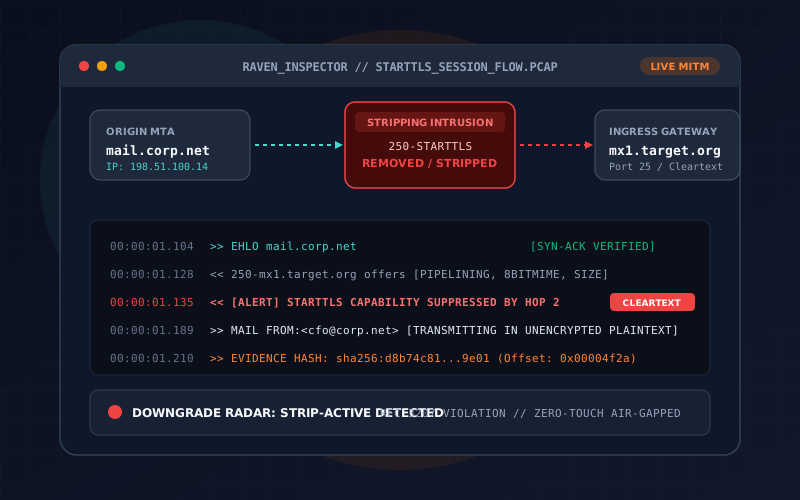 Threat Research
The Anatomy of STARTTLS Stripping in Enterprise Mail Flows
How adversaries exploit voluntary opportunistic encryption, bypass unverified certificates, and silently downgrade email transit security in the wild.
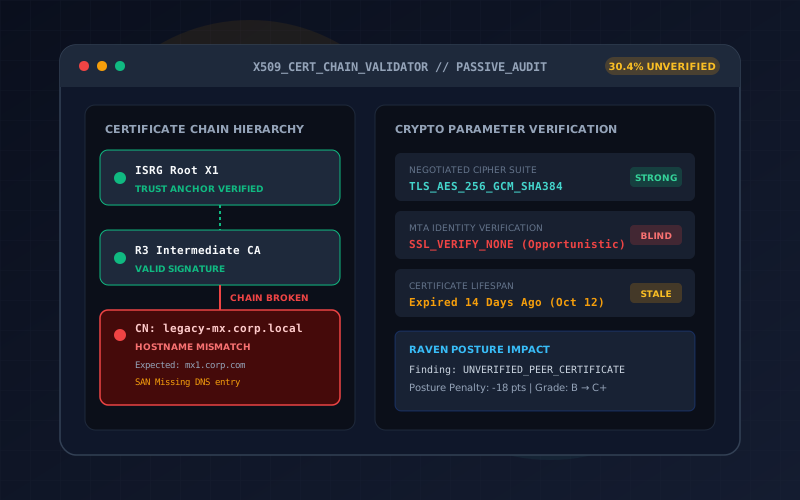 Cryptographic Audit
Why 30% of Global Mail Server Certificates Fail Validation
A deep dive into hostname mismatches, expired trust chains, and why over half of modern MTAs never validate peer identity certificates.
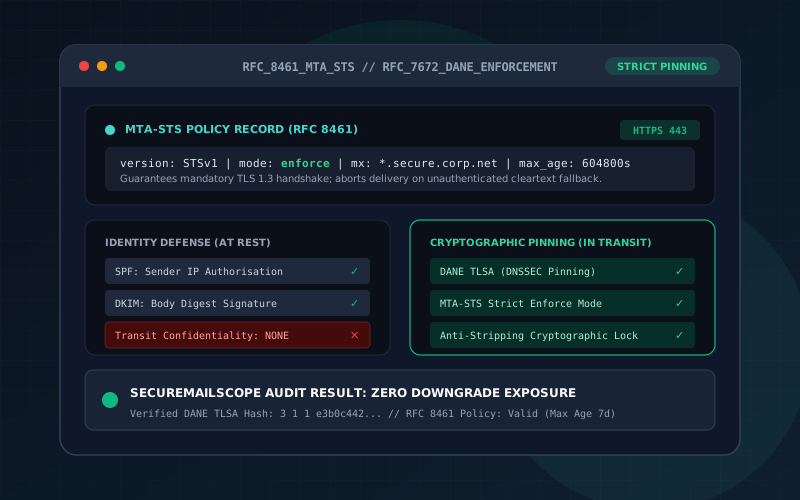 Protocol Standards
Enforcing MTA-STS and DANE: The Missing Defense Layer
Why SPF, DKIM, and DMARC are not enough to protect transit confidentiality, and how cryptographic pinning eliminates active downgrade risks.
X25519 · AES_256_GCM
DigiCert Global Root G2
STARTTLS Stripping Detected
Packet #1,429 [Offset 0x04F2]
Ready to Audit Your Email
Cryptographic Posture?
Drop in a PCAP capture or deploy a passive tap to uncover STARTTLS downgrades, invalid certificates, and weak ciphers across your entire mail path.
FLOWS: 1,429 analyzed
EVIDENCE: SHA-256 sealed
HASH: 7f39b2e81...9c